Get moving sooner
Start with a detailed plan and prepared documents, so your team can focus on implementation.
ISMS Workspace · ISO 27001 software
A practical head start for ISO 27001, with less reliance on extensive consultancy.
Bring your implementation plan, pre-written policies, Statement of Applicability and operational logs into one workspace. Give your team the tools to build, manage and maintain its ISMS.
Technical support included Specialist ISO 27001 services available
Real Showcase screens · Demonstration data · Female English AI narration
Explore what is includedStart with a detailed plan and prepared documents, so your team can focus on implementation.
Keep assessments, decisions and supporting evidence connected and easier to find.
Manage tasks, document changes, reviews and continual improvement in one place.
A clearer route from day one
Reduce the time spent assembling your implementation approach.
Use the detailed implementation plan to set tasks, timelines, owners and dependencies.
Tailor the policies and procedures to your scope, risks and ways of working.
Use the process areas, logs and guidance to turn requirements into work your team can deliver.
The foundations and tools, together
Everything is organised around implementing, operating and maintaining your information security management system.
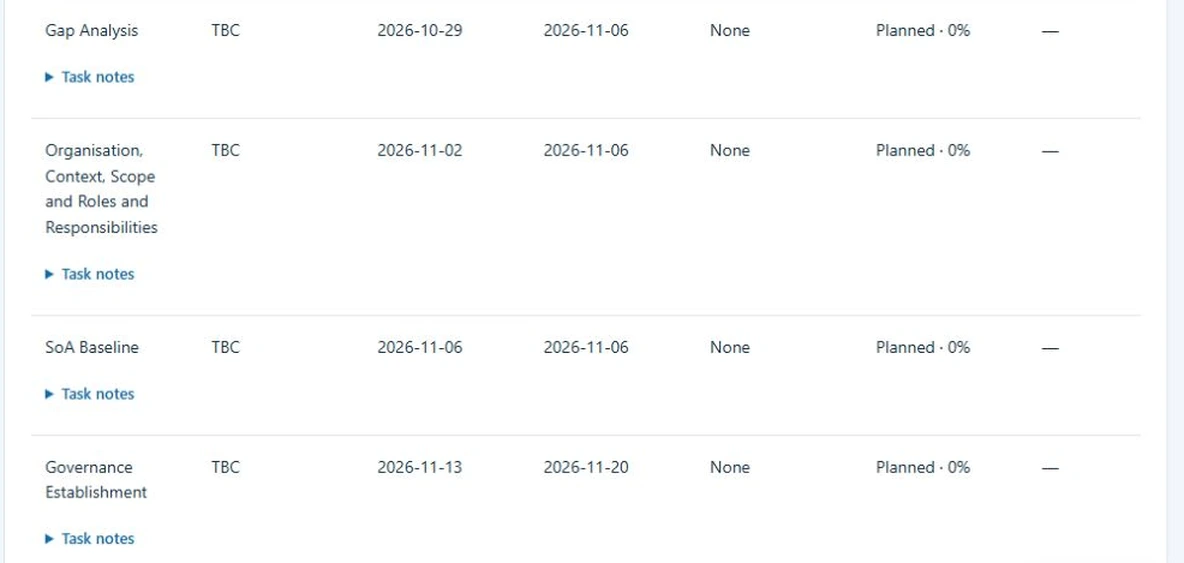
Prepared tasks, ownership, timelines, dependencies and a visual Gantt view keep the work coordinated.
A prepared ISMS Manual and editable policy library give you a practical starting point to tailor, review and approve.
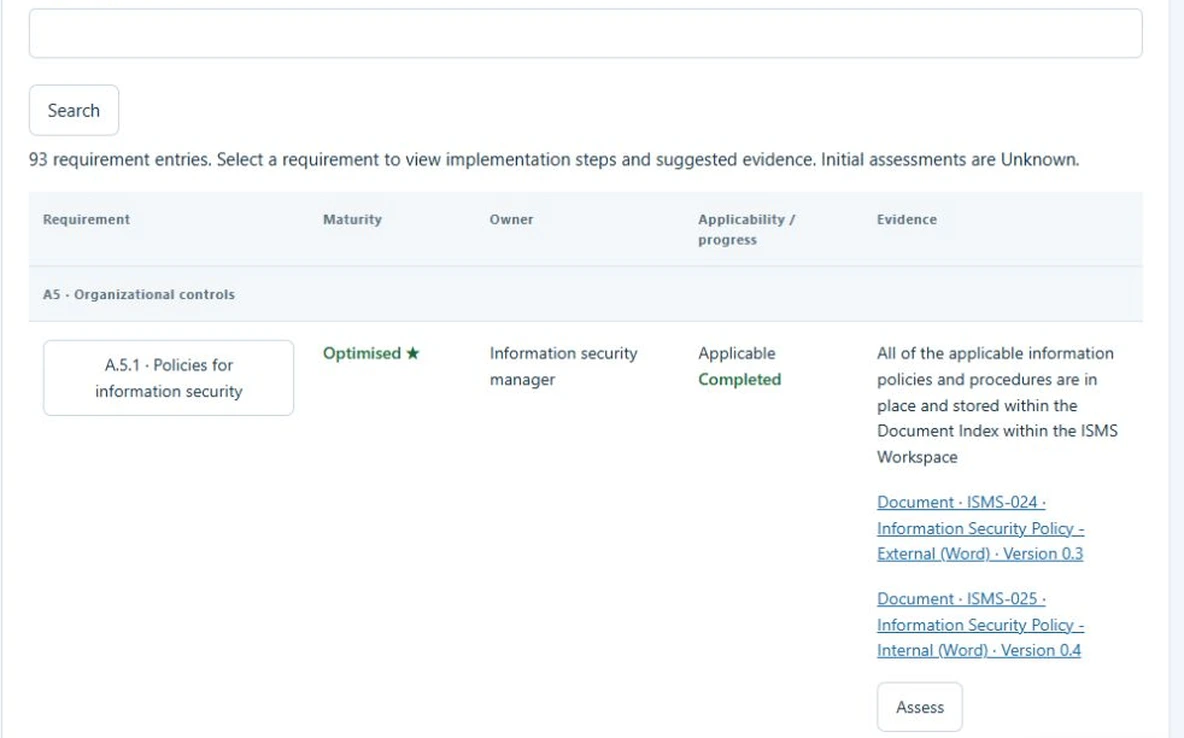
Assess clauses and all 93 Annex A controls. Record applicability, identify gaps and link supporting evidence.
Manage current documents, revisions, approvals and retained history, alongside hardware and software asset records.
Coordinate risk, incidents, suppliers, change, continuity, audits, corrective actions and continual improvement.
Use 39 workspace video guides and a full-transcript workbook to support team understanding, training and everyday use.
Evidence that is easier to work with
Make your ISMS easier to assess and audit.
As implementation moves into ongoing management, your objectives, reviews, governance meetings and next actions stay in the same working environment.
Help your team use the workspace confidently
Supporting videos explain the software and its processes.
Open the relevant guide from a process area, or explore all 39 guides from the Training library. Videos play in a movable window so users can refer to the workspace as they learn.
The workbook brings the full video transcripts together as an online manual and downloadable PDF.
Explore the training in a demo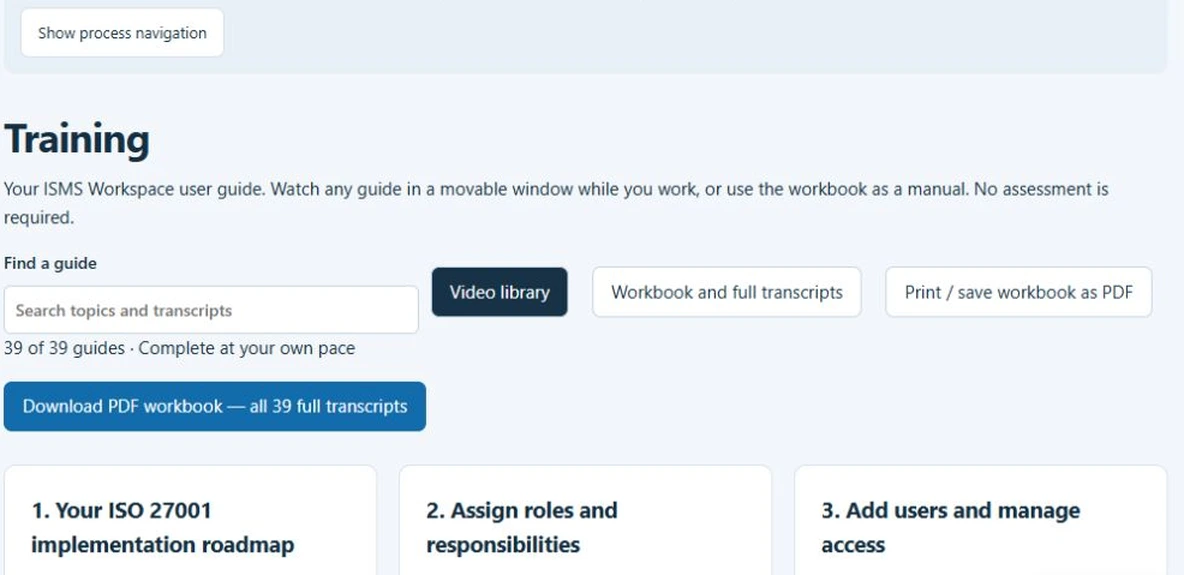
Competitive pricing. Flexible support.
A competitively priced organisation licence, with technical support included.
Use the workspace with your own team and add specialist help where it adds value. ISO 27001 implementation support, internal auditing and ongoing ISMS services are available separately.
Explore additional ISO 27001 servicesWe will explain the workspace, discuss your priorities and provide pricing for an agreed scope.
Your questions
The prepared implementation plan, policy library, process tools and supporting guidance give your internal team a structured foundation. You can progress with your own resources and choose additional professional support for specialist needs.
They are pre-written drafts to tailor to your organisation's scope, activities and risks. Your organisation reviews, approves and operates its own controlled versions.
Technical support for the workspace is included. Additional ISO 27001 consultancy, implementation assistance, internal auditing and ongoing ISMS services can be agreed separately.
Yes. You can work with revised documents and import risks using the supported spreadsheet format. A demonstration can show the workflow and help you plan the migration.
The workspace supports implementation and ongoing management. Your organisation must implement and operate its ISMS; an independent certification body assesses conformity.
Build on a prepared library, tailor it to your organisation and manage the documents and records that demonstrate how your ISMS works.
Accelerate implementation with a full set of draft policies and procedures, rather than assembling the document set from scratch.
Keep a clear record of what changed, which version is current and when it needs review.
Follow a prepared implementation plan that reduces the need to engage professional services to deliver your ISMS.
Move from implementation into a dedicated area for ongoing, task-based management of your ISMS.
Bring requirements, implementation decisions and evidence into one intuitive assessment environment.
Keep the decisions and follow-up that support your ISMS in structured registers, with clear ownership and supporting records.
Move from a list of concerns to a documented assessment and a clear treatment approach.
Give your information security objectives a measurable basis and keep the results alongside the plan.
Give your Information Security Working Group and Management Review Board the tools to coordinate oversight and keep decisions moving.
Manage security responsibilities throughout the employee lifecycle, from joining the organisation to changing roles and leaving.
Bring routine IT security activities into a structured process with records your team can maintain and review.
Know what your organisation relies on and use that information to support both Asset Management and Business Continuity.
Coordinate the activities that keep your security programme current as risks, threats and business requirements change.
Combine structured supplier management tools with AI agents to support supplier risk assessments and assurance work.
The process areas described in the ISMS Manual are brought together in the workspace, with associated documents and records to support day-to-day operation and evidence gathering.
Coordinate ongoing reviews, activities and management tasks.
Record access decisions, reviews and supporting evidence.
Track weaknesses, owners, remediation and follow-up.
Manage workspace roles and time-limited auditor access.
Organise secure development requirements and assurance records.
Coordinate security responsibilities across the employment lifecycle.
Maintain operational procedures and evidence of their use.
Record relevant threats, assessments and response actions.
Bring security requirements into projects and handover.
Maintain inventories, ownership and asset lifecycle records.
Plan awareness activities and retain participation evidence.
Record continuity arrangements, exercises and recovery objectives.
Document proposed changes, decisions and implementation outcomes.
Capture opportunities and track improvement work.
Follow findings through causes, actions and effectiveness checks.
Connect privacy responsibilities with information security activities.
Record incidents, response decisions and lessons learned.
Keep meeting records, decisions and actions together.
Organise management review inputs, decisions and follow-up.
Coordinate the audit programme, findings and supporting evidence.
Maintain applicable requirements, ownership and review records.
Record premises, equipment and physical protection evidence.
Assess, treat and review information security risks.
Identify accountable people, deputies and decision responsibilities.
Organise supplier assessments, assurance and review decisions.
Know what to do and reduce the need for external support as your team works through implementation and ongoing management.
Make the workspace reflect your organisation, its identity and the people who need access.
Give people the access they need for their role and bring auditors into a controlled evidence environment.
Protect the workspace with managed cloud hosting and controlled access.
The ISMS Workspace is an online platform for implementing and managing your organisation's information security management system. It brings your ISO 27001 plan, policies, controls, risks and audit evidence together, so your team can see what needs doing, who owns it, and how work is progressing.
Instead of starting with a blank page, you begin with a detailed implementation plan, pre-written policies and practical guidance. That gives your team a head start, helping you implement faster and reducing reliance on extensive external consultancy.
Turn the implementation plan into a working roadmap. Agree priorities, assign owners, and set timelines and dependencies. The visual timeline helps you coordinate the work, spot delays and keep implementation moving.
More than forty pre-written policies and procedures, including your ISMS Manual, provide the foundation. Tailor them to your organisation, then manage versions, reviews and approvals through the document index. Your team works from a controlled set of current documents.
The built-in Statement of Applicability supports assessment of the management-system clauses and all ninety-three Annex A controls. Decide what applies, record the evidence, and identify the gaps. Clear ownership and linked actions help turn that assessment into progress.
The workspace brings the logs and registers that support your management system together. Coordinate risks, incidents, suppliers, changes and business continuity, with owners, actions and review dates recorded in the right place.
Built-in configuration management helps you track documents, revisions and approvals. Maintain hardware, software and personal-device registers, and connect those operational records with your security processes. Software criticality also supports business continuity planning.
When an audit comes around, your records, decisions and supporting evidence are easier to find. Plan internal audits, provide controlled auditor access, and follow findings through to corrective action. The history shows how your management system operates in practice.
Your team can access thirty-nine supporting video guides from the training library and from relevant workspace areas. The downloadable workbook includes the full transcripts, giving people a practical manual to use as they work.
After implementation, use the ongoing management plan to schedule reviews, track objectives and coordinate governance meetings. Keep actions and continual improvements moving, so the system stays useful as your organisation changes.
The ISMS Workspace is competitively priced, with technical support included. Additional professional services and specialist ISO 27001 support are available when you need them. Your team stays in control of how much assistance it uses.
Give your ISO 27001 implementation a practical head start. Arrange a demonstration with DPS Compliance Hub, and see how the ISMS Workspace can help your team implement faster and manage with confidence.
See how it fits your organisation
Explore the workspace with your priorities in mind, then agree the approach and support that fit your team.